MOLI Single Sign-On (SSO)
Unified Identity and Access Management
One identity. Every system. Managed in one place.
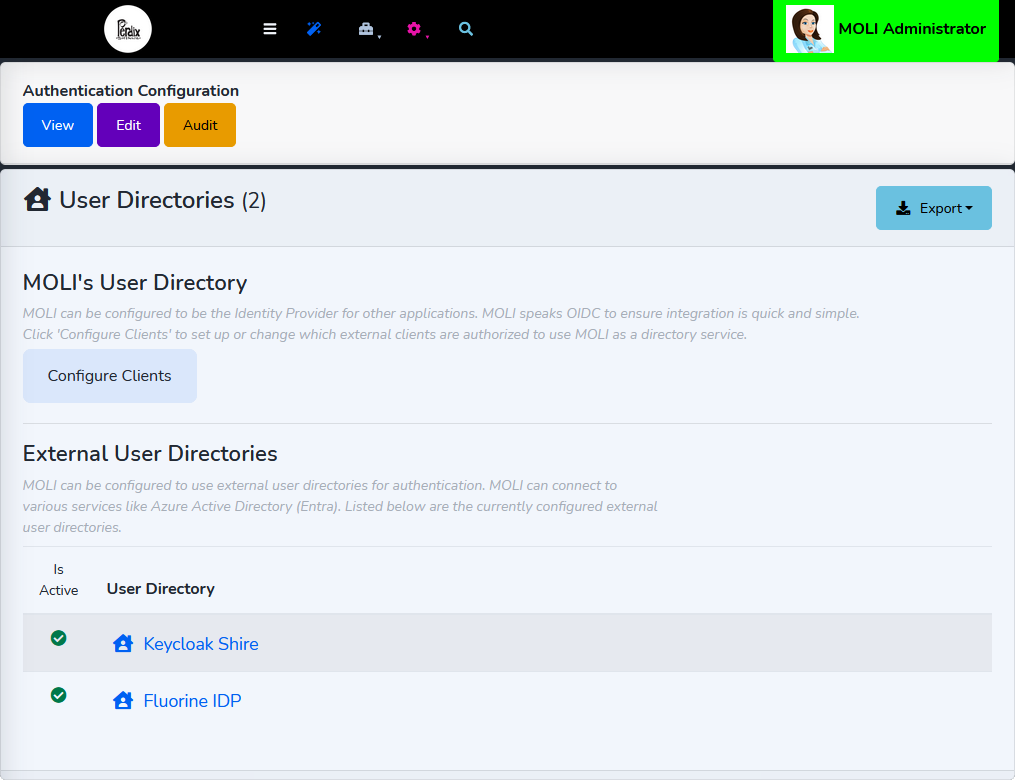
Signing into MOLI via LDAP, or through OIDC / SAML-compliant identity providers like Microsoft Entra, Okta, Auth0, and KeyCloak is supported out of the box.
MOLI can also serve as your organization's identity provider, facilitating the use of one login credential across your organization's entire intranet.
How It Works: MOLI as Identity Consumer
- MOLI's user directory is created as employees log in, with roles and user attributes mapped in configuration.
- Supported Protocols: LDAPS, OpenID Connect (OIDC), SAML 2.0
How It Works: MOLI as Identity Provider
- MOLI's user directory is made available for other services to consume.
- Supported Protocols: OpenID Connect (OIDC), SAML 2.0
MOLI Deployments can also use both modes at once, authenticating users through an external Identity Provider while also providing a User Directory to downstream applications.
This makes the platform flexible enough to integrate with existing enterprise identity strategies while also powering secure authentication for newly built internal applications.
A joint meeting with Perdix Software and your IT practitioner will reveal the correct SSO strategy for your deployment.